NIST releases cybersecurity guide for solo business owners
The final guide translates NIST’s cybersecurity framework into practical steps for businesses without employees, with editable worksheets to help owners get started.

The actual story.
Solo business owners have a new federal resource for figuring out where to start with cybersecurity.
The National Institute of Standards and Technology released the final version of Small Business Cybersecurity: Non-Employer Firms on November 2. Known as NIST CSWP 50, the guide is written for owners without employees and assumes no cybersecurity background.
That includes freelancers, independent contractors, single-member LLCs and gig workers. NIST says the resource is aimed at businesses with relatively simple technology needs, with guidance that can also help as an operation grows.
The publication replaces NIST’s 2016 small-business information-security guide. Its scope is narrower: helping the smallest businesses apply the agency’s Cybersecurity Framework 2.0, rather than addressing small businesses of many sizes. This is the final release, following an April public draft.
The guide’s starting steps include:
• Turn on phishing-resistant multifactor authentication where available, especially for email, banking and other sensitive accounts.
• List the devices, software and services the business depends on.
• Back up important data, protect those backups and test them.
• Keep software current across devices and applications.
• Prepare an incident-contact list and keep a paper copy available.
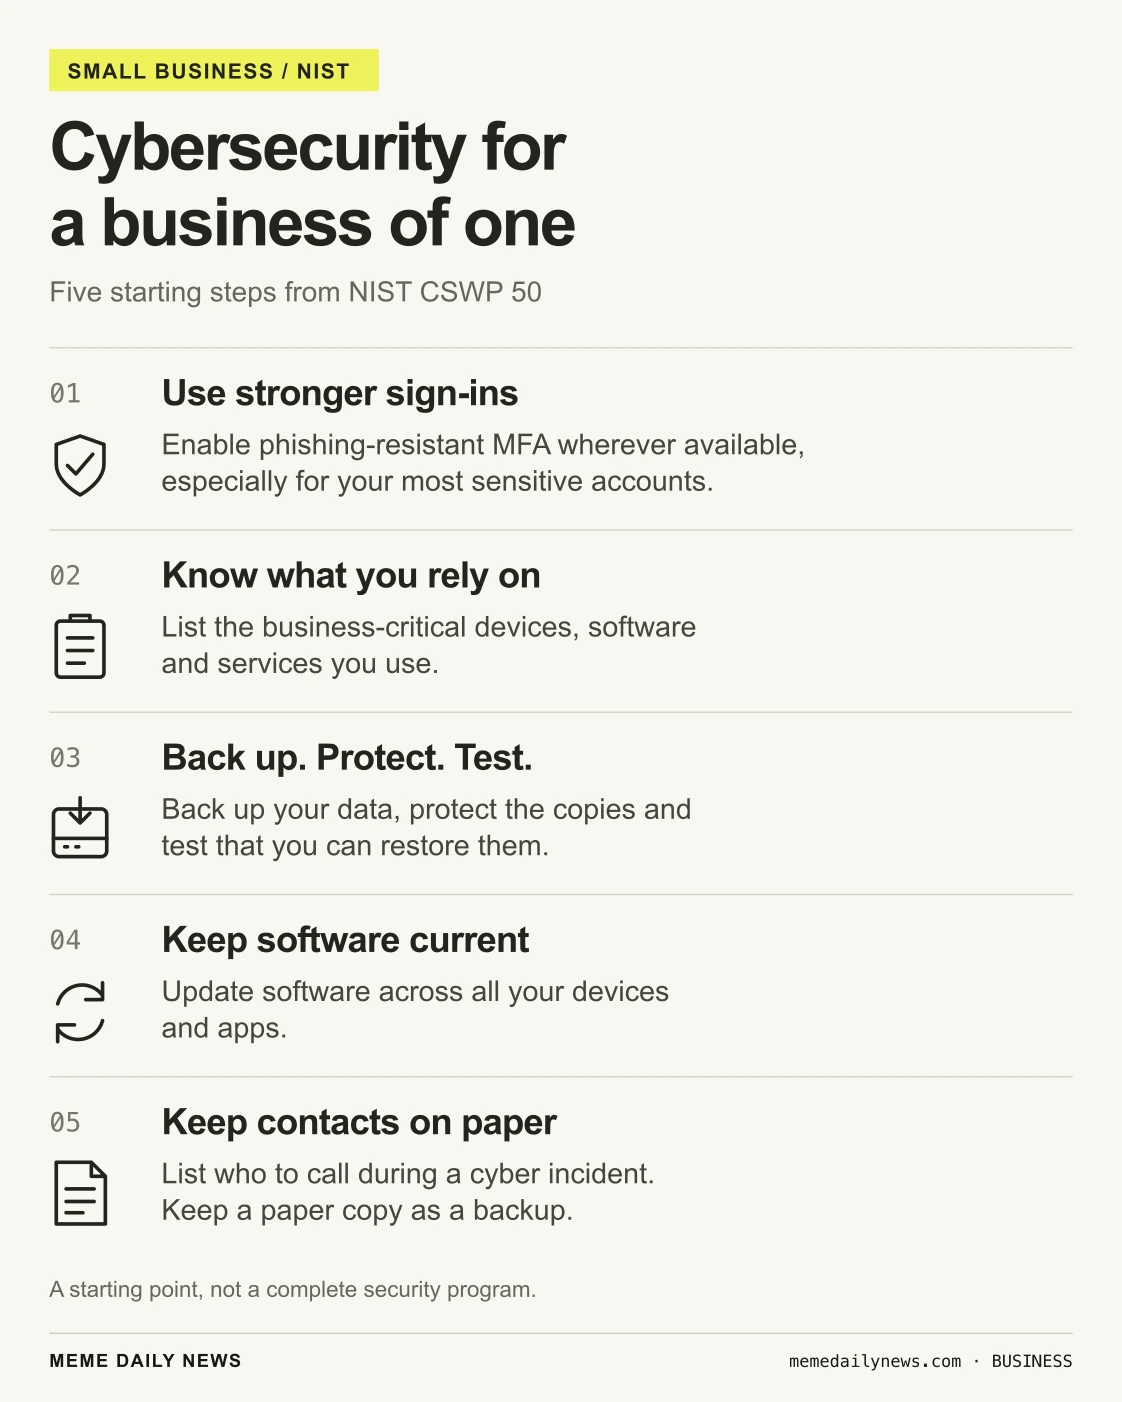
Those recommendations appear near the beginning of the free guide. Later sections explain why each action matters, how to begin and what to consider as the business expands.
NIST also provides an Excel companion with editable worksheets and three hypothetical businesses: a lawyer, a home-workshop e-commerce seller and a marketing and sales consultant. Owners can use the materials to organize their planning instead of starting from a blank page.
The guide is a starting point, not a complete security program. NIST cautions that each business’s needs depend on its industry, resources and contractual or regulatory obligations.
The guide is a starting point, not a complete security program. NIST cautions that each business’s needs depend on its industry, resources and contractual or regulatory obligations.
Receipts, not rumors.
- NIST · announcement, November 2
- NIST CSRC · final release notice
- NIST · publication record and companion resources
- NIST · final CSWP 50 guide
Read the original reporting: NIST
The reporting above provides context. Illustrations are editorial interpretations, not source photographs.
What’s your take?