Brotli Security Flaw Prompts Updates Across Node.js, Bun, Envoy and .NET
A Brotli vulnerability prompted security updates across Node.js, Bun, Envoy and .NET, showing how one shared component can affect several developer stacks.

The actual story.
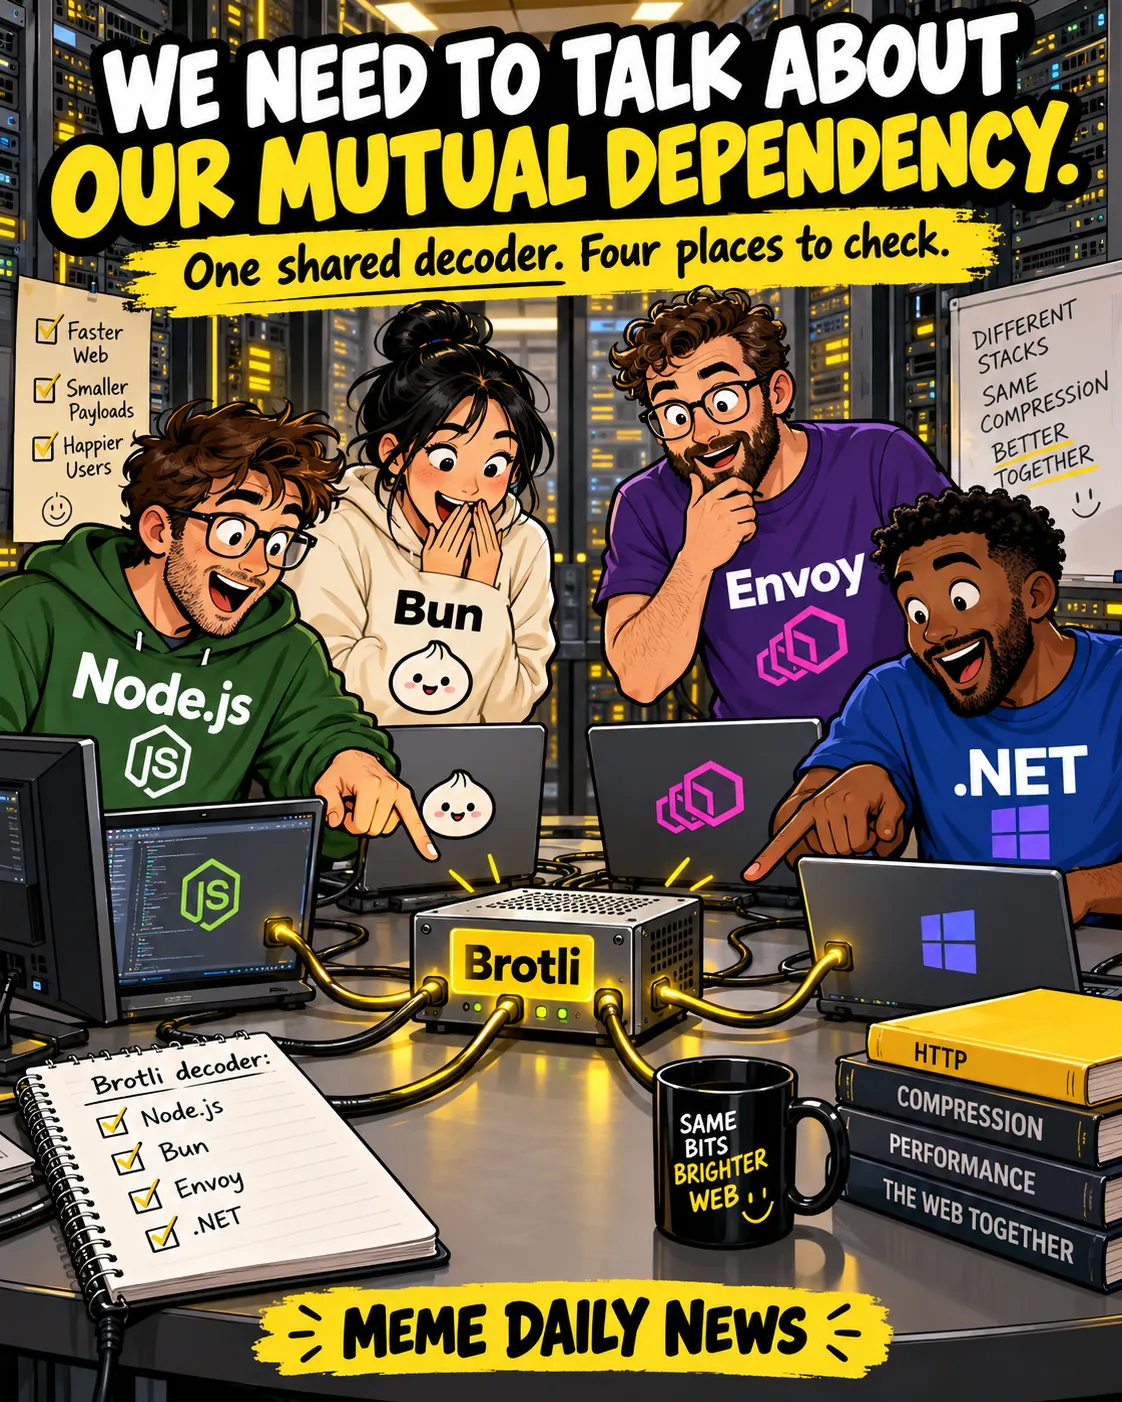
A security flaw in the Brotli compression library has prompted fixes across Node.js, Bun, Envoy and Microsoft .NET. The vulnerability can allow malformed compressed data to corrupt memory when affected software decompresses it, potentially causing crashes, exposing information or enabling code execution. Node.js released its fix on October 21.
The connection is a shared dependency: different products incorporate the same underlying decoder. That means fixing one application or runtime does not necessarily resolve exposure elsewhere in a company's software stack. The affected versions and configurations differ by product, and the reviewed advisories do not establish active exploitation.
Teams should check each vendor's guidance, update affected deployments and verify the patched version is actually running. Packaged applications may need to be rebuilt and redeployed. An upstream patch is only useful once it reaches the systems handling the data.
Check the deployed software, not just whether a fix has been released.
Receipts, not rumors.
Read the original reporting: Node.js; Bun; Envoy; Microsoft .NET
The reporting above provides context. Illustrations are editorial interpretations, not source photographs.
What’s your take?